
Cyber Attackers
An attacker can be a single person or a group of individuals with goals, motivation, and capabilities. As a coin has two faces same attackers have, some attacker does attack for fair reasons and some for their greedy needs. The result of the attack decides what type of attacker has committed the crime, its desire, motive, and goal of crime or cyber-attack. It has become mandatory to differentiate between types of attackers.
We are surrounded by the digital and hyper-connected components that allow attackers to access our sensitive information. The attack can be conducted from any side; it may be data breaches for private information, banking data, retail data, government and private organizational data, health to entertainment, and various other sectors which are not immune from cyber-attacks.
“Cyber attackers are considered as cyber threat actors that perform cyber-attacks having some goals, motivation and capabilities.”
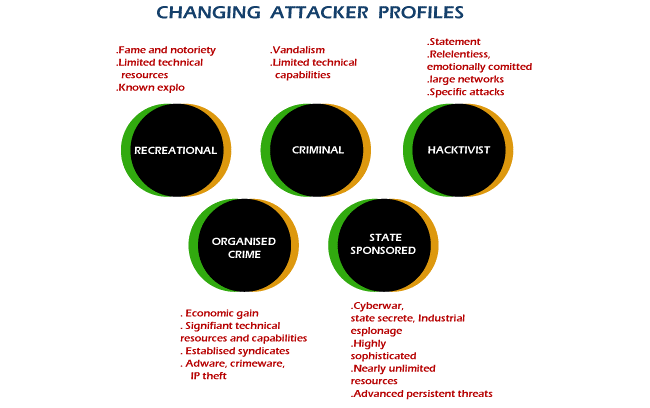
Cyber-attacks are conducted by cybercriminals or cyber attackers who are classified under these categories:
- Hacktivists
Hacktivists are one type of cyber attackers acting as an individual or group of individuals for the political agenda, social ideology, and religious belief. These are not considered the same as cybercriminals because they work as injustice fighters. Hacktivists introduced a new term, "hacktivism," digital obedience (here, hacking is done for a reason or cause).
Hacktivism – This has become very popular in recent years as they associate with the high-profile campaign and isn't always illegal. Hacktivists disrupt undeniable means in hacktivism to cyber-crime against private and government individuals. Basically,
Hacktivism = Hacking +Activism
Hackers don't need to have technical knowledge when hacking activity is considered a misuse of technology for social or political purposes. Without technical skills, an individual can cause damage, for example, by promoting controversial material on the internet.
- Hacktivists and hackers are both interrelated, but their hacking aims differentiate them. For example, a general hacker breaches the network security and steals data for financial purposes or to prove its ability. Still, a hacktivist does hacking to achieve a political and social outcome where he public those files instead of selling them.
- Hackers are money and fame-minded, but hacktivists are frame-minded.
- Legally, both terms are the same; hacktivists commit cybercrime regularly to effect potential penalties. Hacktivists attack the victims (organizational and individual) where they represent viewpoints and values they disagree with due to which their behavior is considered immoral.
- Hacktivism is debatable as it has good intentions, but it's illegal too as it can cause financial damage to its victims.
- There are various types of hacktivist organizations, but two are notable as follows:-
- Anonymous – These individuals hide and are named as anonymous, who are rarely identified. Still, cyber security authorities have managed to arrest them as they target large organizations and high-profile public figures such as politicians, people in business, actors, and others. They have performed successful attacks against them several times.
- Wikileaks - This is an international non-profitable hacktivist organization started by Julian Assange(director). This organization is a media organization behind the important information leak in recent years, including the Afghanistan war, "the intolerance network", 16000 procurement requests posted on united embassies worldwide, and many more. Website – https://wikileaks.org, and it has a complex legal status.
Types of hacktivism
- Website defacement
Website defacement means using the website to deface by getting their(hacktivist) point access. This method is picked up by the media that consist of a message that discredits or embarrasses an organization. This attack prevents the proper functioning of the website.
- Doxxing
This type is an important tool to punish anonymous types of people. Doxxing is a method of discovering a person's identity and public it on the online platform.
- Anonymous blogging
Hacktivism is a broad term carried out to change public opinion, and it is easily committed by anonymous blogging as it is part of free speech on the internet. Anonymous blogging is used by criminals to explain their attacks, and opinionated bloggers and whistler blowers also use this in some countries without free speech.
- DDoS attack
The full DDoS attack is a distributed denial-of-service attack used to disturb normal web traffic. Hacktivists used this attack to take the website offline by sending so many visitors to a website simultaneously, due to which servers become overwhelmed. This attack is generally designed to harm large organizations with minimal effort.
- Leaking information
This is simply stealing sensitive information by hacking private computer system and publishing it online to cause embracement or discredit the victim. These attacks are illegal and allow imprisonment to the hacktivist.
- Website mirroring
Hacktivists use website mirroring for financial purposes or to avoid geo-restrictions. It's simply creating a mirror website of the entire original website and putting it on the internet with a different URL. With this method, people visit restricted websites in countries (heavily censored internet access).
- Cybercriminals
Cybercriminals are generally individuals or groups of people who commit cyber-crime with a profitable intention. Here criminals attack the individual or organization for stealing their personal and private information by using computers and the internet as their tools. They use computers for their mission in the form of targets, weapon and an accessory.
- Inside threats
The inside threat came within an organization internally from employees or former employees and third parties, including temporary workers, employees, contractors, and customers. This is an internal threat to an organization that can be malicious, negligent, and accidental.
| Malicious | These are the inside organizational attacks caused to access and harm an organizational data, system, or IT infrastructure. These are justified by employees and ex-employee in seeking revenge. |
| Accidental | These are the inside accidental threats done by inside employees like deleting an important file or sharing confidential information to the outsider beyond the company's terms and conditions and keeping on-stake of the company’s security. |
| Negligent | This type of insider attack is not illegal. Still, it can be dangerous as employees share and save the company's valuable data to the data storage application (public cloud application) so that they can work from home. Due to this, companies have strict policies for external file sharing. |
- State-sponsored attackers
State-sponsored attackers are responsible for state-sponsored cyber-attacks, which have become a common part of the cyber security landscape. These types of attackers are employed through their military and government authorities. The government-funded these attackers indirectly because the government doesn't want to frame itself if any attack was detected. State-sponsored attackers detect vulnerabilities and exploit them before holes are patched, and sometimes they are undefeatable. In recent months, organizations(small, medium, large), small businesses, NGOs, governmental and political parties have dealt with state-sponsored attackers.
State-sponsored attackers perform some of the state-sponsored cyber attacks:-
- Finding secret political information, secret private and organization and discovering cooperative secrets.
- Attack on companies and critical infrastructure damages their defenders and diminishes their defensive capabilities.
- Spreading wrong information is one of the common cyber-attacks for disrupting political opinion within a state (improving and defaming public opinion on political parties that affect the elections).
- To test the capabilities of the attacker and readiness of advisory.