
Types of penetration testing
Penetration testing is the collection of techniques utilized to resolve the various issues of the system and test, analyses and give a solution. So, understanding penetration testing is incomplete without learning about the several types of penetration testing.
In the cyber industry, for providing cyber security in different aspects like network, web application, mobile application, cloud storage, database, and client security, these types of penetration testing are there:
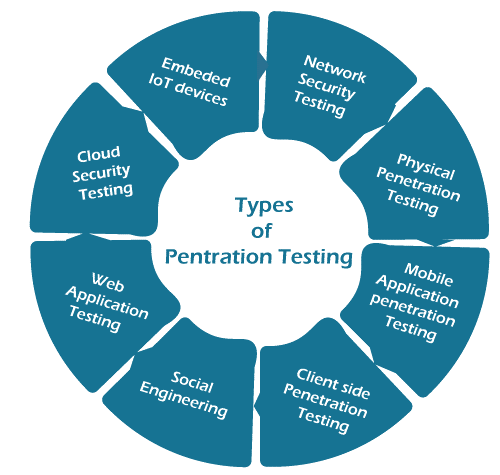
Network security testing
This penetration testing is to find the vulnerabilities or weaknesses in the network infrastructure anywhere (on-premise or cloud environments like Azure and AWS penetration testing). This test is required to protect the data and security of your application. It is crucial with many areas like encryption, outdated security patches and configurations, which are tested and checked. Network security testing is divided into two parts:
- External Pentest – This attack is done by an outsider having access to the internet with no previous knowledge of the internet. An outsider tries to exploit the vulnerabilities from outside and break into the system to access internal data and the system.
- Internal Pentest
This testing is concerned with testing the application in an internal environment, i.e. within the organization. But external threats are riskier than internal ones because internal security breaches result from a breach in the external security protocols. To get into the organization, the attacker first breaches the outer layer and holds its presence already within the network.
List of already done network pentests:- DNS footprinting
- SSH attacks
- Tests on proxy servers
- Testing routers
- Firewall bypasses
- Evasion of IPS/IDS
- Scanning and testing open ports
Physical penetration testing
Physical penetration testing can determine whether attackers can gain unauthorized access to the server room, which can serve as an entry point into the corporate network. This penetration is required to detect the vulnerabilities and issues in physical assets like cameras, sensors, barriers, barriers and others that may lead to a breach. It also takes care of how the organization deals with physical security threats such as tailgating, social engineering, badge cloning and many more. In the end, these can generate a report to the organization with information about discovered physical security flaws and remediation suggestions.
Mobile application penetration testing
This testing discovers mobile application vulnerabilities but doesn't include mobile API and servers. Mobile application penetration testing uses these tests:-
| Static analysis | It is used to reverse engineer to extract elements like metadata and source code. |
| Dynamic analysis | Dynamic analysis is done during the runtime of the application. The tester finds the vulnerabilities by extracting data from the RAM or bypassing controls. |
Client-side penetration testing
It's simply the testing done on client devices like web browsers and workstations to detect software vulnerabilities because these can easily exploit the client's device. These kinds of attacks are identified in client-side pentest:-
- HTML injections
- Malware infections
- Cross-site scripting attacks (XSS)
- Clickjacking attacks
- Form hijacking
Social engineering
Social engineering attacks result from unwanted advantages of human psychology taken by attacks. Hackers exploit human nature to break security breaches and access the system. In social engineering penetration testing, the tester manipulates human nature and coaxes individuals to reveal sensitive information. This information is useful for planning further attacks and penetrating the system. A list of some social engineering attacks are:
- Eavesdropping
- Tailgating
- Dumpster diving
- Phishing attacks
- Masquerading attackers as vendors, colleagues and contractors
- Bluesnarfing
Web application testing
The entire application (including business logic and custom-built functionalities) is tested to protect against data breaches and other attacks. This testing is required to uncover the security lapses in customer relationship platforms, websites, e-commerce platforms, content management systems and others. Web applications are the source of huge data, and with the rise in web applications, lots of data transmission takes place that becomes an easy target for cyber-attacks. Everyone (organization and individual) dealing with web apps regularly conduct this act to keep up with the latest attack methodologies and security flaws. Web application penetration testing is required for some of the following vulnerabilities:
- Misconfigured web servers
- Spoofing MAC address
- Wireless encryption
- Network traffic
- Cross-site scripting (XSS)
- Weak credentials
- Website database
- Distributed Denial of services attack – DDoS
- SQL/ code injection attack
Steps followed in the web application penetration testing process are:
- Surveillance: In this step, they gather information regarding the application, like resources and operating system (OS) used.
- Discovery: Detection of vulnerabilities
- Exploitation: For gaining unauthorized access to the application, it uses the detected vulnerabilities and its pools of data
Cloud security testing
The cloud environment is used to save the data and is different from traditional on-premises environments. Cloud used as a database platform shares security responsibilities with the organization; therefore, cloud pen testing requires specialized skills. Penetration testing uses these cloud testing specialized skills and experience to scrutinize different aspects of the cloud-like APIs, encryption, configurations, various databases, storage and security controls.
Embedded IoT devices
Embedded or IoT devices must need penetration testing because of their long life cycles, power constraints, remote locations, regulatory requirement and many more functionalities. It includes devices like oil rig equipment, medical devices, smart watches, automobiles, home appliances etc. In penetration testing, experts perform a thorough communication analysis and client/server analysis to identify defects that matter most to the relevant use case.
Penetration testing services
Penetration testing is provided in two types of services: manual and automatic.
Manual penetration testing
A security consultancy or contractor can manually perform penetration testing. Hackers conduct systematic and extensive testing by agreeing on a specific scope with the client. During testing, ethical hacker attempts to breach the organization’s security, search for the vulnerabilities and after that, prepares a detailed report on them. The report depicts what the hacker has discovered and suggestions for remediation.
| Manual Test Pros | Manual Test Cons |
| Generic vulnerabilities are easy to discover via automated tools, but it used to uncover business logic vulnerabilities. It can detect zero-day vulnerabilities. It can stimulate complex attack campaigns, including multiple threat vectors. The human testers use automated tools to combine automated scans with manual exploration and analysis. Before generating the scanning report, the penetration tester validates or checks all the findings because false positive is not a concern in this case. | Each penetration test is required a high cost and large efforts From the organization's point of view, setting up a penetration test is a complex process as it requires a detailed definition of scope, contracts and coordination with internal stakeholders The test result depends on the tester's skills as an unskilled tester can miss important vulnerabilities and insights. The unskilled tester lacks relevant experience in the organization's industry or technology stack Manual testing only performs the test on a quarterly or annual basis, which leaves the organization open to zero-day threats or vulnerabilities. This can affect the changes to production systems. |
Automatic penetration testing
Penetration testing can be automatic, which provides a service of testing with the new model & known as PTaaS – penetration testing as a service. This service is for organizations, providing an automated platform for performing penetration testing on their system. PaaS services conduct the testing by using technologies like dynamic application security testing (DAST), automated vulnerability scanning and fuzzing without human intervention. Automatic testing does the same as it finds vulnerabilities and security weaknesses and attempts to exploit them. It gathers all the information about possible targets, identifies the potential entry points, tries to break in either actually or virtually, and makes a final report of all the findings to the organization's security team. This testing has variable moving parts, but still, it saves time and produces better penetration test results than manual testing. Automated penetration testing is an effective tool that reduces the high risk to the enterprise from real-world attacks and mitigates the vulnerabilities.
| Automated testing Pros | Automated testing Cons |
| Automatic penetration testing makes testing procedures practical for companies without or with a security team. It works with a flexible payment method and lower costs. It's most services include pay-per-use pricing and subscription too. It is a self-service model, too, showing all the test details to the client. It provides a web interface to the client on which system and at which frequency the test is performed. After testing automated report is generated that suits the organization's needs with specific compliance requirements. | As compared to manual testing, it has more hale positives Can’t identify business logic vulnerabilities The use of encryption in the testing system can complicate the use of PaaS services. It makes the organization more responsible regarding testing as it determines the testing schedule and reviews finding independently. To run automated penetration in the cloud environment, the cloud providers require permission to run them and limit the testing to a specific window time. |