
Elements of vulnerability management
Vulnerability management is the process or program that consists of identifying, classifying, remediation, and mitigating security vulnerabilities.
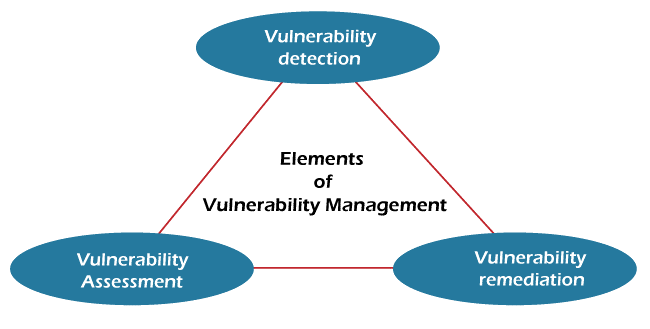
The whole process is included in the three core elements of vulnerability management, where vulnerabilities are detected, assessed and remediate with the help of various tools and testing. Elements of vulnerability management are as:
- Vulnerability detection
- Vulnerability assessment
- Vulnerability remediation
Vulnerability detection
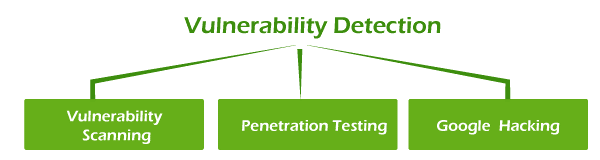
Without detecting or identifying vulnerabilities, it's impossible to patch them and provide security to the system. To provide security against vulnerability, vulnerability detection is done by three methods:
- Vulnerability scanning
- Penetration testing
- Google hacking
Vulnerability scanning
Vulnerability scanning process help in classifying and detecting system weaknesses and security holes in communication equipment, networks and computers. To identify network, system, application and security vulnerability, the scanning process is used to find the commonly known "vuln scan”. This automated process is performed by an organization's IT department or third-party security service provider. Attackers also scan to find any weakness in the system so they can exploit it for their benefit.
For the scanning process, a scanner (software) is used which discover and identify vulnerabilities resist due to flawed programming and misconfiguration within a network. Scanning is done by using a piece of software running from the organization or person inspecting the attack surface in question. The scanner also compares the details about the target attack surface by using a database or its references like
flaws, packet construction anomalies, coding bugs, potential paths to sensitive data and default configurations can be exploited by attackers.
The scanner scans the device and software to check for possible vulnerabilities within the scope of engagement. Further, it generates a scan report, which is analyzed and interpreted by the organization's experts to improve its security posture.
Some of the popular scanning tools are:
- Probably
- Acunetix
- Manage Engine Vulnerability Manager plus
- Rapid 7 Nexpose
- Solar winds network configuration manager
- Tripwire IP 360
Categorization of network vulnerability scans based on use-cases:
- Scanning methods
- Intrusive vulnerability assessment
The intrusive scanning method highlights the security risk and an impact of an exploited vulnerability. This scanning can create issues for customers and employees of an organization by disrupting processes and operational systems in the network; therefore, it should be used with caution. In this, an attack plan is created after vulnerabilities are discovered during scanning. - Non-intrusive vulnerability scan
Using a non-intrusive method, no actual vulnerability exploitation occurs during this process; it identifies a vulnerability and generates a report so the user can fix it. Scanner finds out the occurrence of vulnerability in the given conditions.
- Intrusive vulnerability assessment
- Scanning types
- Internal vulnerability scan
This type of scan targets the internal enterprise network, which finds vulnerabilities to avoid damage. It also makes the organization tighten its security and protect its system and applications not exposed by external scans. Suppose a hacker finds a security hole in the system or application. In that case, it can leave the enterprise system prone to damage, so an internal vulnerability scan of the system's internal network is essential to protect it. - External vulnerability scan
It scans all the exposed areas in the IT ecosystem that use the internet or are not restricted for internal use. Such exposed areas accessed by users and customers are websites, networks, applications, ports and systems. - Environmental vulnerability scan
This vulnerability scan is special and deployed for multiple technologies like websites, mobile devices, IoT devices and cloud-based services. Here scanning is based on the specific environment of the organization's technology operations.
- Internal vulnerability scan
Penetration testing
Penetration testing (pen test) is the type of vulnerability detection tool used by security experts to find and exploit security vulnerabilities in a computer system. It’s a kind of attack purposely used to identify any weak spot in the system regarding preventing the system from the attackers taking advantage of it.
With the right intention and scope, penetration testing can drive into any aspect of the system. With the pen test, experts ensure the system is robust enough to bear the authorized or unauthorized attacks and examine the range of system roles. This is like hiring someone to apply techniques, tools and processes like attackers do to discover and demonstrate the vulnerabilities/weaknesses in the business in a system.
Google hacking
Google hacking, known as Google docking, in which Google search engine is used by hackers/attackers to locate security vulnerabilities and submit queries to search engines to find sensitive information lying on web pages that Google has indexed. It also refers to finding security vulnerabilities in applications indexed by Google. Google hacking is not bound to search through the search engine but can be practised on any major search engine.
Vulnerability assessment
Vulnerability assessment is a one-time project with a time boundation (start and end date). Some of the characteristics of vulnerability assessment are the same as penetration testing, but vulnerability assessment is not a scan. Penetration testing finds the weak spots in the system's security but vulnerability assessment followed by penetration testing identifies cyber security threats and risks via automated vulnerability scanning tools, which provide information to the information technology and information security teams to mitigate and prevent cyber security threats.
Vulnerability remediation
As the name defined in this element, vulnerabilities are remediated (can be corrected), but before that, vulnerabilities need to be discovered and followed the process.
- Discover
- Prioritize
- Remediate
- Monitor
Remediation workflows depend on the scanning and communication tools to function. Penetration testing and vulnerability assessment are responsible for some vulnerability remediation as these produce test reports and outline how to fix them. These reports are helpful for security teams to rank flaws by severity, and the team can patch the critical flaws first.
Traditional remediation can be responsible for leaving the system vulnerable for longer than necessary if it increases the mean time to respond (MTTR).
How to build a vulnerability management program?
There are certain steps to build, establish and strengthen an organization's top-notch vulnerability management program.
- Assemble a team
- Acquire the right tools
- Keeping a current or comprehensive inventory of assets
- Develop an "obsessive focus on visibility."
- Threat landscape should be cross-referenced with the environment
- Knowing about application, assets and risk tolerance
- Remediate, communicate and report
- Be more aggressive with scanning
- Deliberated and documented workflow
- Track KPI’s
- Create a bug bounty program
- The expectation is set and adjusted over time
- Program performance should be reported to stakeholders
Challenges in vulnerability management program
- Incomplete asset inventory
- Identifying vulnerabilities
- Prioritizing vulnerabilities
- Timely remediation of vulnerabilities
- Tracking the vulnerability management process
Vulnerability management best practices
- Regularly scanning of vulnerabilities
- Scanning of endpoints of network and every device too
- Owners are assigned to critical assets
- All scans and their result are documented
- Ensuring security assessment and risk-based prioritization of the patching process
- To ensure continuous security assessments, correct training is provided to the IT team.
- Updation of security baselines is maintained and mapped with compliance requirements.
- Review, measure and define the metrics of the program
- Mitigation tracking is deployed in the vulnerability management program
- The vulnerability management program is centrally visible