
×

Process of Penetration Testing

Companies or organizations use penetration testing manually or automatically to identify the system's vulnerabilities. All companies need to protect their assets and themselves from cyber-criminal attacks by updating their security measures simultaneously.

At the same time, it is difficult to know which and how the method is being used in the attack. Organizations hire skilled, ethical hackers to help identity, update and replace the defective or attacked parts of their system. Ethical hackers use penetration testing to detect weaknesses in the system because it is unique from other cyber security evaluation methods.

Depending on the organization's infrastructure and operation, penetration testing can be adapted to any organization or industry, but this follows a certain process that creates a set of results to help the organization. Let’s discuss the process of penetration testing step by step.

Stages of penetration testing

The penetration testing process starts long before a simulated attack. An ethical hacker is allowed to study the system to explore its strength and weakness and to identify the right tools & strategies to break into the system. Penetration is based on the structured procedure and performed step by step such as follows:-
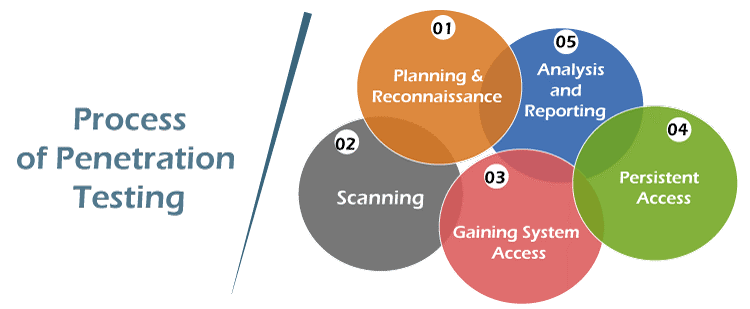
Process of Penetration Testing
  • Planning and Reconnaissance

This is the first step in the testing module, where planning and preparation are executed depending on the organization's needs. This step can be short or lengthy according to the requirement. Here, clients and testers properly aligned the test's scope, goal, and execution. They must have some knowledge about the tests like:

  1. What kind of test are they running?
  2. Who has to be aware about the test is running?
  3. With how much information and access permission tester should start the work
  4. Some of the other important details ensure that the test is a success
  5. Emails address and names of the company's employees to a network topology with the IP address, among others
  6. For the planning and searching process, these methodologies are used:
    • Dumpster diving
    • Social engineering
    •  Network scanning
    • Domain registration information retrieval
  • Discovery/ Scanning

After the planning phase, the discovery and planning phase is designed to identify the threats and how the target system responds to all the attempts at intrusion.

For the scanning purpose of initial vulnerabilities, the tester uses automated testing tools. This phase is necessary to obtain all the information about the system accurately, which includes usernames, passwords, and all the data in the system. This process is called fingerprinting. It probes and scans the ports where vulnerabilities exist. Here three types of discoveries are carried i.e.

Host discovery = It discovers the open ports on the devices

Service interrogation = In this, all the services running on ports are discovered by interrogating them

Network discovery = It includes the discovery of servers, additional systems, and other devices   

  • Gaining system access
    After learning about all the system vulnerabilities, pen-testers mimic an actual attack in a simulated and controlled environment. This phase analyses how far a tester can get into an IT environment without detection.
    After controlling a device, the tester performs a web application attack or a physical attack like cross-scripting or SQL injection attack. This pen tester infiltrates the system or infrastructure by exploiting security weakness, demonstrating how the target gets deep into the environment.    
  • Persistent access
    In this step, once the penetration tester gets access to the device and holds the access or their presence as long as possible, it also simulates an attack long enough to accomplish & replicate malicious hacker goals. This phase is designed to obtain the maximum level of privileges and access to many systems as much as possible and network information by identification of data or services are available.
  • Analysis and reporting
    It is the last stage of penetration testing, where the testing team prepares a detailed report describing the entire penetration testing process. The pen tester writes all the detail of each step, consisting of how the pen tester took steps to in-filtrate systems and process, clean up after stress test, details of all the vulnerabilities, and suggestions for fixing the vulnerabilities.

    Reporting is important for both parties because it is the base of working of the IT staff and non-technical managers; therefore, it is suggested to prepare a separate report. One part is on general explanation (executive report) and the other on a more technical aspect (technical report).  

Related Topics

Penetration Testing Tools

Penetration testing is applied to counterfeit cyber-attacks to assess the network's security, server, or web application to improve and prevent real threats' exploits by repairing vulnerabilities. Ethical hackers test to determine...

7 minutes read.

Process of Penetration Testing

Companies or organizations use penetration testing manually or automatically to identify the system's vulnerabilities. All companies need to protect their assets and themselves from cyber-criminal attacks by updating their security...

3 minutes read.

FINRA

Introduction Payment cards need PCI DSS standard for security, but apart from it, there are other financial services like share market, stocks, bonds, etc. require security. So, for this, security experts...

9 minutes read.

Types of hackers

Types of hackers Cyber security is the protection shield for technology users as it fights several cyber-attacks and helps in their prevention. There are various types of cyber attackers present around...

5 minutes read.

Types of penetration testing

Penetration testing is the collection of techniques utilized to resolve the various issues of the system and test, analyses and give a solution. So, understanding penetration testing is incomplete without...

6 minutes read.

Cyber Security Fundamentals

Cyber security fundamentals represent basically for what purpose cyber security came into existence. Cyber security is beneficial to individuals, organizations, or large business firms, but it offers the same benefits...

3 minutes read.

Vulnerability Assessment

Introduction In most cases, vulnerability management is considered a vulnerability assessment. Still, these are different terms as the “vulnerability management” process manages to find and remove vulnerabilities, and “vulnerability assessment” is...

8 minutes read.

Cyber Security Vulnerability

Introduction Cyber security is the security provided to the internet to protect and secure valuable information. Security is needed against the system's threats, risks, exploits, and vulnerabilities. Here we goanna understand what...

6 minutes read.

Jobs and roles in cyber security

Cyber security is one of the booming careers and desired fields in the cyber industry. Cyber security is a vast ocean of knowledge and a big domain that consists of...

7 minutes read.

Types of security policies

Policies act as a protection field for the business, organization, and individual users to allow them and protect their rights. Security policies are meant to provide security for the technology...

9 minutes read.

Penetration Testing

Introduction When software or a system is designed, it is not fully secured as human creates it, and human is a mannequin of mistakes. In the cyber industry, no device, system...

7 minutes read.

Canary in Cyber security

Introduction Cyber security is meant to provide security to the cyber/ internet/ IT world. It aims to secure the organization against cyber-attacks by using various security products. Not just data, applications...

5 minutes read.

Eavesdropping attack in cyber security

Introduction Eavesdropping is a technique of finding someone's conversation details for personal benefit. When an ongoing communication between two people is interrupted, or a third person tries to listen to that...

6 minutes read.

ISO - International Standard for Organization

* Abbreviation is ISO of International Standard for Organization derived from the ancient Greek word ísos which means equivalent or equal. ISO develops and publishes a wide of industrial, commercial,...

6 minutes read.

Types of social engineering attacks

A trap made by hackers by using deceptive psychological manipulation methods (taking advantage of human behavior variations like fear, excitement, or urgency). Social engineering is one kind that covers the...

7 minutes read.

Cyber security policies

Introduction Security experts design security policies to protect the enterprise, employees, staff, and business from various threats. The written documents consist of planning to protect the company from undesired issues and...

4 minutes read.

Cyber security tools

Cyber security is an essential part of the internet industry to protect confidential data and financial records, and a system needs security. Cyber security analysts provide various tools to keep...

16 minutes read.

Functions of Cyber Security

Let’s learn about the Cybersecurity Framework's five Functions that are the key pillars of wholistic and successful cyber security programs. These five functions result from the highest level of abstraction...

3 minutes read.

Applications of cyber security

Cyber security terms define the process of safeguard implemented on the device that working in a network (online) is safe and secure. In this digital era, personal and private networks,...

4 minutes read.

Types of cyber security vulnerabilities

The user must know all the vulnerabilities to understand cyber security vulnerabilities and build a vulnerability management program. Here are some of the common types of cyber security vulnerabilities: System misconfigurationsThe...

8 minutes read.