
×

Data Encryption Standards

The Data Encryption Standards was introduced by the National Institute of Standards and Technology. A Feistel Cipher is implemented in DES. The Data Encryption Standards was developed by the company named IBM in the early 1970s and the development of this system is based on the inventions of Horst Feistel.

The popularity of the Data Encryption Standard (DES) has been discovered to be slightly declining because of the discovery that DES is susceptible to very strong attacks. Data encryption standard usually works based on block cypher, and it encrypts the data in 64bits each. The key is 56 bits long.

History of Data Encryption Standards

The National Bureau of Standards first studied the security of US government computers in 1972 and found a need for a government-wide standard for encrypting sensitive, unclassified data. This is when DES was born.

How does Data Encryption Work?

As a result, the original 64-bit key is reduced to a 56-bit key by throwing away every eighth bit of the key. DES is built on substitution (also known as confusion) and transposition, two key components of cryptography (also called diffusion). Each of the 16 steps in DES is referred to as a round. In Data Encryption standards, all the 16 steps are a single round.  The stages of substitution and transposition are carried out in each round.

  • The 64-bit plain text block is sent to the initial Permutation (IP) function in the first phase.
  • The first permutation is applied to plain text.
  • The encryption process now includes 16 cycles for both LPT and RPT.
  • After reuniting LPT and RPT, the combined block is sent through a Final Permutation (FP).
  • This procedure generates 64-bit ciphertext as the result.

Steps in Data Encryption Standards

There are three steps in the Data Encryption.

  • Initial Permutation
  • Key Transformation
  • Expansion Permutation

Initial Permutation

Before the first round, the initial permutation (IP) occurs only once. As seen in the graphic, it makes suggestions for how IP transposition should go. Nothing more than a bit-position juggling game with the initial plain text block is being done here. All other bit locations are subject to the same regulation.

Simple bit-position juggling with the initial plain text block is all that is involved in this. The same principle applies to all other bit places shown in the illustration.
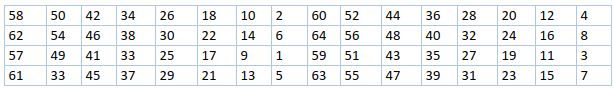
Data Encryption Standards

Key Transformation

As mentioned, the initial 64-bit key is reduced to 56 bits by throwing away every eighth bit. Consequently, a 56-bit key is accessible for each. A procedure known as key transformation is used to create a unique 48-bit Sub Key from this 56-bit key throughout each round. The 56-bit key is split into two parts, each of 28 bits, for this purpose. Depending on the round, these halves have a circular left shift of one or two locations.

For instance, if the round number is 1, 2, 9, or 16, the circular shift is carried out by two positions for additional rounds. The figure displays how many key bits are shifted per cycle.
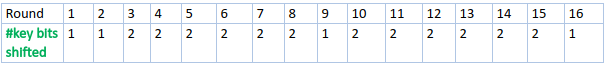
Data Encryption Standards

48 of the 56 bits are chosen after the proper shift. The table is depicted in the image below for choosing 48 of the 56 bits. For instance, bit number 14 shifts to the first position following the shift, followed by bit number 17, and so on. We can see that the table only has 48-bit positions if we look at it closely. To decrease a 56-bit key to a 48-bit key, bit number 18 is eliminated along with 7 other bits (bit number 18 will not appear in the table).
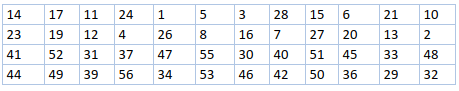
Data Encryption Standards

Expansion Permutation

The term "expansion permutation" refers to the permutation of bits as well. This occurs because the 32-bit RPT is split into 8 blocks, each of which has 4 bits. Then, after adding 2 extra bits to each 4-bit block, each 4-bit block from the previous phase is increased to a corresponding 6-bit block. While producing output, this process causes the input bit to expand and be permuted. The 56-bit key is compressed to 48 bits during the key translation procedure. The 32-bit RPT is then expanded to 48 bits by the expansion permutation method. The 48-bit key and 48-bit RPT are now XORed before the output is given to the S-Box substitution.


Related Topics

Uses of Blockchain

Nowadays, there are a lot of applications for Blockchain technology exist. The main use of Blockchains is to serve as a distributed ledger for cryptocurrencies like Bitcoin; by the end...

5 minutes read.

ElGamal Cryptosystem

The ElGamal cryptosystem was first discovered by Taher ElGamal in the year of 1984. It is based on Discrete Logarithm. When the discrete logarithm cannot find the assumption at the...

6 minutes read.

Demur-rage currencies in Blockchain

One of the key concepts of Blockchain technology that may be extended and re-understood is currency. Currency, often known as a digital token, allows for quantifiable transfer mechanisms. Demur-rage money...

4 minutes read.

Feistel Cipher in Cryptography

What is Feistel Cipher? A Feistel Cipher is a structural model that is used to build various symmetric block Ciphers similar to DES. This structural model can be self in veritable....

4 minutes read.

IDEA: International Data Encryption Algorithm

The International data encryption algorithm (IDEA) is a symmetric key algorithm that is designed to convert text into an unreadable text format. It uses a 128 bits block size and...

3 minutes read.

Key Areas of Blockchain

As we know that Blockchain is the backbone of the technology of digital cryptocurrency (Bitcoin). The Blockchain contains all transaction records which are stored in a distributed database; it even...

3 minutes read.

Sending and Receiving Bitcoin

The goal of this part is to show you how to get started with Bitcoin in a simple way. 1. Get to Know Bitcoin Bitcoin has certain unusual characteristics. It behaves similarly...

4 minutes read.

How to Block Hashes Work in Blockchain

Working of Block Hashes in Blockchain It is a concept for storing data digitally. It will be available to everyone (publicly). Whoever wants to see it will be able to see...

4 minutes read.

History of Blockchain

History of Blockchain: Satoshi Nakamoto modeled the first Blockchain and explained the details of how a technology was well-found to enhance digital trust, given the immutable and decentralization aspect that...

2 minutes read.

Blockchain Terminologies

Blockchain Terminologies: In this section, we will learn about a few terminologies used in Blockchain technology. Understanding these terms will help you to learn the blockchain technology in an efficient...

3 minutes read.

Blockchain Block Hashing

Blockchain is the main technology used for digital cryptocurrencies like Bitcoin. Blockchain consists of a database that has all the records of digital events that have taken place or all...

3 minutes read.

Advantages of Cryptography

Cryptography is the practice of secure communication in the presence of third parties. It allows for the secure exchange of information between two or more parties and can be used...

4 minutes read.

Project Ideas on Blockchain for Professionals

We have moved on from the days when Blockchain was solely employed in the context of cryptocurrencies. It is currently used in a broader range of applications, and it will continue...

4 minutes read.

What does Blockchain contain?

A Blockchain is a network of interconnected blocks. Four components make up a block: NonceMerkle tree rootPrevious HashThe timestamp A cryptographic hash of the contents from the preceding block is contained in...

3 minutes read.

Smart Contracts

What is a Smart Contract? A smart contract is a self-executing computer program. It is a decentralized computation program, which directly controls the transfer of digital assets between different parties under certain pre-defined...

5 minutes read.

Consensus Algorithms in Blockchain

We all know that Blockchain is a decentralized distributed network that provides immutability, privacy, security, and transparency. Considering the absence of a central authority to authenticate & verify transactions, the...

4 minutes read.

Kerberos in Cryptography and Network Security

Kerberos is a system that is used for managing user authentication. With the help of Kerberos, the user can access their service without remembering multiple authentication passwords. It is not...

3 minutes read.

Blockchain Double Spending

When the money is spent twice, we call it double-spending. We know any transaction can occur in two different ways 1st way is offline mode and 2nd way is online...

3 minutes read.

Blockchain Explorer

Blockchain Explorer A blockchain explorer is an online webpage similar to Mozilla and Google Chrome, which allows users to browse and explore information about blockchain technology. All bitcoin and ether users depend on blockchain explorer...

3 minutes read.

Blockchain DAO

In Blockchain, the full form of DAO is Decentralized Autonomous Organization. As the DAO full form says, the organization is both decentralized & autonomous. Sometimes DAO is also known as...

3 minutes read.