
Jobs and roles in cyber security
Cyber security is one of the booming careers and desired fields in the cyber industry. Cyber security is a vast ocean of knowledge and a big domain that consists of practices, systems, technologies, secure networks, processes, devices and data from cyber-attacks, cyber threats and unauthorized access.
Levelling up in data and generating it at high-speed need protection. For this protection purpose, companies need skilled security professionals to safeguard organization information and computer network. To play this role, knowledgeable people are selected for different posts. So here are some of the cyber-security jobs and roles in cyber security careers in this field.
These cyber security job roles can be categorized on the following parameters:
→ Educational qualification of the candidate
→ Candidate professional work experience
→ Holder of cyber security certification
→ Specialization in a certain area (some candidates prefer coding & some prefer managerial posts)
These parameters enable setting a cyber security career path and deciding the salary for the top paying roles in cyber security jobs.
Different types of cyber security jobs in India
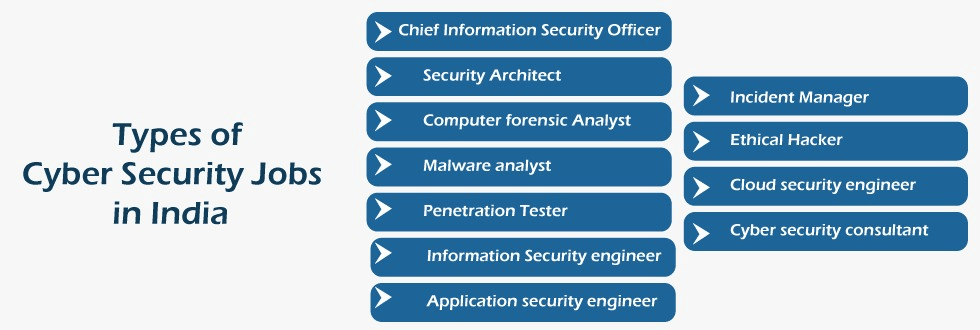
Chief information security officer
| Skills of chief information security officer | The skills required for this job & role are as follows: → Business expertise → Risk management → IT experience → Presentation skills → Strong communication skills → Incident management and supervisory skills |
| Certifications of chief information security officer | For this job following certification is required: - Certified Information Security Manager (CISM) - Certified Information Systems Security Professional (CISSP). |
| Salary of chief information security officer | The approximate salary of a chief information security officer is between 2 crores to 4 crores. |
Security Architect
| Skills of security architect | A company’s security system is nothing without security architecture because they are the person who is responsible for designing the network and computer security architecture for the company. The security architect understands the need for company security and, on this base, creates a design & works in collaboration with the programming team to build the final structure. Besides this, they also work in researching, planning, designing elements of security, developing policies, security procedures and reliable actions regarding security issues. |
| Certification of security architect | The certificate required to be a security architect is CompTIA Security+ and CISSP (Certified Information Systems Security Professional). These are beneficial for every learner. |
| Salary of security architect | The approximate salary of the security architecture begins at Rs 17 lakh per annum. |
Computer forensic Analyst
| Skills of computer forensic analyst | Forensic analysts analyze cyber attack cases to retrieve data and gather digital evidence. They also work on manipulated data, recovering digital data or stolen data. The following skills are required for this role are: → Bachelor degree → Work experience in the related field → Strong communication skills → Networking knowledge → Understanding of law → Knowledge of criminal investigation → An analytical mind |
| Certification required for computer forensic analyst | - Certified computer examiner (CCE) - Certified Forensic Computer Examiner (CFCE) |
| Salary of computer forensic analyst | The approximate salary of the computer forensic analyst starts at RS 7 lakh per annum. |
Malware analyst
| Skills of a malware analyst | The malware analyst job role requires these skills: → Graduation or degree in information technology or computer science → At least two years of work experience in a relevant field → C and C++ language knowledge → Strong communication and presentation skills → Knowledge about the operating system like Windows, Linux and UNIX → Knowledge about using tools like OllyDbg, IDA Pro, RegShot and TCP view is required |
| Certification of a malware analyst | The job of malware analyst requires this certification: - GREM – GIAC Reverse Engineering Malware certification |
| Salary of Malware analyst | The approximate salary of a malware analyst is about Rs. 5lakh.ss |
Penetration tester
| Penetration tester skills | Some of the essential skills required for the penetration tester are as follows: → 1-4 years of experience in information security → Knowledge of black box testing → Having good networking skills → Aware of the languages like C, C++, Python, Java and Perl is also vital → Good communication and presentation skills → Strong reporting → Knowledge of Linux, Windows, and UNIX operating system |
| Penetration tester certification | This role requires this kind of certificate: - Certified Ethical Hacker (CEH) - Certified Expert Penetration Tester (CEPT) - Offensive Security Certified Professional (OSCP) |
| Salary if a penetration | The approximate salary of the penetration tester is about Rs 2,151 258. |
Information security manager
| Skills of an information security manager | This is also important in detecting and preventing cyber threats within the company (data, application, system and network). A business can be in debt if they fail to protect sensitive customer information and violate protection laws, therefore, detecting loopholes in the system. Large organizations hire them to prevent company data, systems and networks from being hacked. |
| Salary of an Information security manager | The approximate salary of the information security manager in India starts from Rs 15 Lakh per annum to Rs 16 lakh per annum. |
Cyber security engineer
| Skills of a cyber security engineer | The post of cyber security engineer is designated to strengthen technology initiatives and take them to the next level. Cyber security engineers are integral to the system that creates and executes secure network solutions. This role is in high demand and the a demand-supply gap in the required workforce capabilities for this position. Therefore companies need in-depth knowledge and experience for this role. A cyber security engineer has to prove himself to bring to the table. Some other skills required for this post are: → Strong presentation and communication skills → Knowledge of computer languages like C, C++, Python, and Java (essential) → Good understanding of management and architecture of the operating system → Good networking skills |
| Certification for a cyber security engineer | - Certified ethical hacker certification - CompTIA Security + certification - Advance certification for the experienced person for levelling up |
| Salary of a cyber security engineer | The approximate salary of the cyber security engineer in India is from Rs 10 lakh to 11 lakh per annum. |
Application security engineer
| Skills of an application security engineer | Application security engineers require in-depth knowledge and expertise in the privacy and compliance aspects of third-party applications like AWS or Azure. They are responsible for dealing with the stability of an organization's external and internal applications. An organization hires these cyber security professionals when it has to install and integrate some software into its day-to-day operation and prevent cyber threats that disrupt the integrity of the whole application infrastructure. |
| Salary of an application security engineer | The expected salary of an application security engineer in India is about 9 lakh per annum. |
Incident manager
| Skills of incident manager | The incident manager is a managerial and executive role after obtaining suitable credentials. An incident manager is appointed to handle something that goes wrong, decide what to do in the situation and take full ownership of the result. He is proficient in solving security incidents and determining all the resources in an organization. Skills required for this role are leadership aptitude and problem-solving abilities and further enhance or demonstrate your skills. |
| Salary of incident manager | Approximately % to 6 lakh per annum |
Ethical hackers
| Skills of an ethical hacker | Ethical hacker posts are valuable and important posts in an organization regarding the protection and prevention of data. This role required lots of intuitive knowledge and skills to reveal hackers' or attackers' logic. An ethical hacker does the legal hacking in an organization that tests and picks the vulnerabilities of systems, networks and applications. They conduct the hacking test in a defined way regularly (monthly, daily, weekly or quarterly) depending on the organization's need. In the cyber market today, ethical hackers are gaining momentum as they provide insider information regarding the protection of the organization from high-level cyber-attacks |
| Salary of an ethical hacker | Ethical hacker salaries depend on their working experience. A person with 0-3 years of experience can make 3.5 lakh per annum, but industry-experienced and certified professionals can earn as high as Rs 15 lakh per annum. |
Cloud security engineer
| Skills of a cloud security engineer | Cloud service engineers provide recommendations on service design and application development. It requires building, maintaining and continuing improvement in the cloud-based network and system in the industry. They handle the organizational cloud computing environment, their platform, core infrastructure, and software. |
| Salary of a cloud security engineer | Approximately 7.9 lakh per annum |
Cyber security consultant
| Skills of cyber security consultant | Companies hire cyber security consultants on a contractual basis, but for this post, a person must have cyber industry experience with professional certification. They have to showcase their potential to employers as they have to independently deal with the issues reacted to cyber security in a business. |
| Salary of cyber security consultant | Approximately 6.5 lakh per annum |
Conclusion
Apart from them, there are plenty of other roles that go unfiled. For examples:
- Firewalls
- Information risk auditors
- Security analyst
- Cryptologists
- Computer device development professional
- Security device development professionals etc.
An organization or business or a wide range of industries like government retail, BFSI sector, banks, hospitals and education demand cyber security professionals regarding their data or customer information protection from attackers. This type of job demand is rising with time in this digital era. The major challenge we face is not meeting the demand for cyber security professionals in the various sectors. This is due to a lack of courses, training, low salary and low interest of people in cyber security.