
Eavesdropping attack in cyber security
Introduction
Eavesdropping is a technique of finding someone's conversation details for personal benefit. When an ongoing communication between two people is interrupted, or a third person tries to listen to that information without user knowledge, this method of secretly listening to a conversation is known as eavesdropping. Eavesdropping in Hindi “Kaan Laga ke sunna” means "listen to someone words silently”.
Being every work transferred on the online platform, millions of transaction takes place digitally. Utilization of the internet needs data as input like sensitive personal information into the website to sign up, make a purchase, scroll and many other things. So, eavesdropping in the form of sniffing takes this data from websites. Hackers develop such special programs or software to seek out and record parts of sensitive data communication from insecure networks. Users cannot analyze these sniffing tools, but with the help of advanced cryptographic tools, these info packets can be analyzed.
"Eavesdropping is the insidious cyber security attacks as they are difficult to detect or analyze that they are coming." Unknowingly when connected to a network, users feed sensitive information like accounts, credit debit card details, passwords or the content of email messages etc., to an attacker.
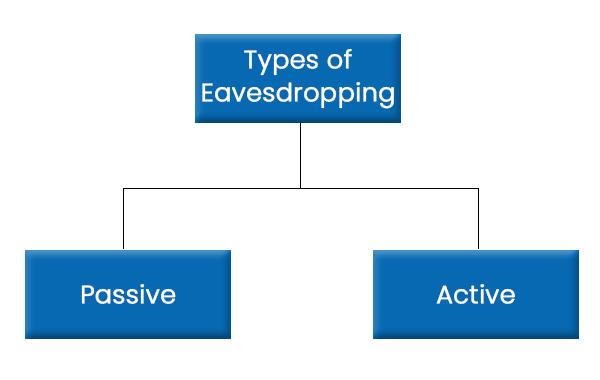
There are two kinds of eavesdropping attacks: active eavesdropping and passive eavesdropping.
→Active eavesdropping (hackers enable to disguise themselves)
→ Passive eavesdropping ( in this, hackers listen to the communication or data passing through the network
Some consequences of eavesdropping attacks are data fraud, financial loss, identity theft, loss of security and monetary misfortune.
Working on eavesdropping attack
A hacker uses different methods to perform an eavesdropping attack. Still, the common thing in all of them is the involvement of the communication channel and listening to the transmitted information.
When a connection between client and server is weak or not secure, it increases the chance of eavesdropping. When there exists an insecure network due to the absence of encryption in transferring data, devices and applications aren't up to date or the presence of malware in the system.
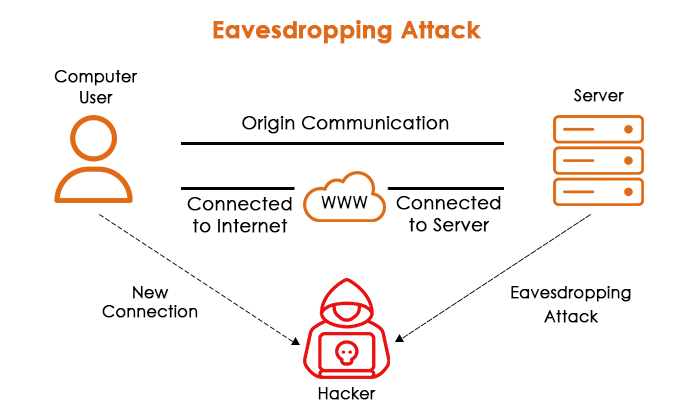
A connection is a setup between client and server over an insecure network (over a typically Wi-Fi hotspot or website not running the HTTP protocol). The information in terms of data packets travelling across the network could be intercepted. The hacker created programs that sniff and listen to the communication without acknowledging the user. This process is called eavesdropping.

Methods of eavesdropping attack
Transmission link – In communication, the receiver link's sender is tapped to eavesdrop. This tapping can be done with the radiofrequency transmission or a wire that includes electrical wires, unused or active telephone lines or ungrounded electrical conduits. Some transmitters work remotely, but some can operate continuously.
Listening post – A listening post is a method of eavesdropping in which bugs are placed on the telephone to hear the conversation. The user is unaware that the hacker has installed or applied such a program or bug in the telephone. When the telephone makes a call or rings (picked up), the recorder is triggered and records the whole conversation and automatically turns off when the call ends. Hackers can do this anywhere with the availability of voice-activated equipment to eavesdrop & record every activity.
PickupPickup devices – Attackers use pickup devices such as microphones and video cameras to pick up images and sound and use power sources in the target room. It also dispenses with the requirement for the aggressor to get to the space to re-energize the gadget or supplant its batteries.
Open network – When clients interface with the open organization in which they don't need a password and can't utilize encryption to communicate information create circumstances for aggressors to listen in. Hackers interface & screen client actions and sneak on correspondences that happen in the organization.
Powerless passwords make it simpler for the hacker to acquire unapproved admittance to client accounts, indirectly giving them a course to incorporate frameworks and organizations.
Eavesdropping attacks example:

Cyber-attacks look for sensitive information that can be sold to the dark web for a criminal purpose. This information includes business strategies, call recordings and financial details. Here are a few examples of eavesdropping attacks:
- Spouse ware attack is one kind of eavesdropping attack under which victim smartphone is trapped for their location and keep a check on all of their activities.
- Smart voice recognition assistants are best suitable or vulnerable to eavesdropping. For example, Google Home and Amazon Alexa have an "always on" mode feature that threatens users' privacy.
- When users connect to the public unsecured Wi-Fi networks freely available at railway stations or cafes, hackers fetch user login credentials to hack their email ids, Facebook accounts & card details over the public network.
- Wireshark eavesdrop attack registered in 2011caused on android smartphone. Wireshark was a sniffing program in which attack authentication tokens were sent over an unencrypted Wi-Fi network. When a smartphone is connected over this unsecured network, it results in Wireshark stealing, viewing, modifying or even deleting all the personal or confidential information.
- iOS are the most secure device, but in 2015 it suffered from an eavesdropping attack. In this, over 25000 iOS apps were vulnerable to eavesdropping attacks as this app had a bug in the open source code library AF Networking. With this bug in the app, HTTP encryption could be taken down.
Prevention of digital eavesdropping
- Encryption
Encryption is the major method cyber security experts use in which data is encrypted before it is transferred using digital networks for security reasons. This data is scrambled before it is sent to the receiver with the motive that if a third party tries to read the data, it only sees a string of gibberish. The information received by the receiver is decrypted with the encryption key to scramble the message and retrieve the information securely and safely. - Building more secure networks
Digital eavesdropping can be prevented by building secured networks for companies that help withstand hackers' attacks. For this purpose, firewall and anti-virus software are used to secure all the information that travels between the network's nodal points. - Contributing to digital literacy
Using the internet, people must be aware of keeping data secure or believe in using protection methods. Cyber security experts must explain the basics of cyber security to other employees who use the company's digital network.
Protection against these attacks adopted by a company
- Authentication
High-level authentication must be used by IT or security teams for incoming network packets. Standard and cryptographic include:- TLS (transport layer security)
- Open PGP
- IPsec (Internet protocol security)
- S/MIME (Secure/ multipurpose internet mail extension)
- Network segmentation
This network is segmented into parts, so traffic cannot flow from one segment to the next. It makes organizations limit their resources to those who want to access them. For example: In an organization, every department is different, and cyber security experts can't interfere in any department without permission or with an issue to be resolved.
- Network monitoring
In cyber security, network monitoring is essential. In this network, abnormal activities or traffic are monitored. Attackers and security teams use the same eavesdropping software to detect vulnerabilities. This process can be simplified using deploying an intrusion detection system and detection system or response solution.
- Physical security
By implementing or using physical security measures in the office spaces, organizations protect their data and users because physical bugs on desks, phones, and many other devices and unauthorized people are crucial to prevent. - Shielding and protecting
The risk or result of eavesdropping via computer radiation can be prevented by installing shielding and security measures. For example, TEMPEST is used to protect computers. It also enables the organization to block unintended radiation while keeping the organization and user data secure.
- Update and fix programming
Weaknesses and loopholes in the system are being exploited to target clients and associations. So to reduce this, security patches must be applied by updating the system and guaranteeing that all the product is fixed promptly.
- Cyber security awareness
The reason for happening eavesdropping attack is clicking an unwanted link in an email by an employee. Employees click this link which installs the malware. Training and educating the employees (including phishing risks and how to avoid becoming a victim is crucial) is the solution to creating cyber security awareness.